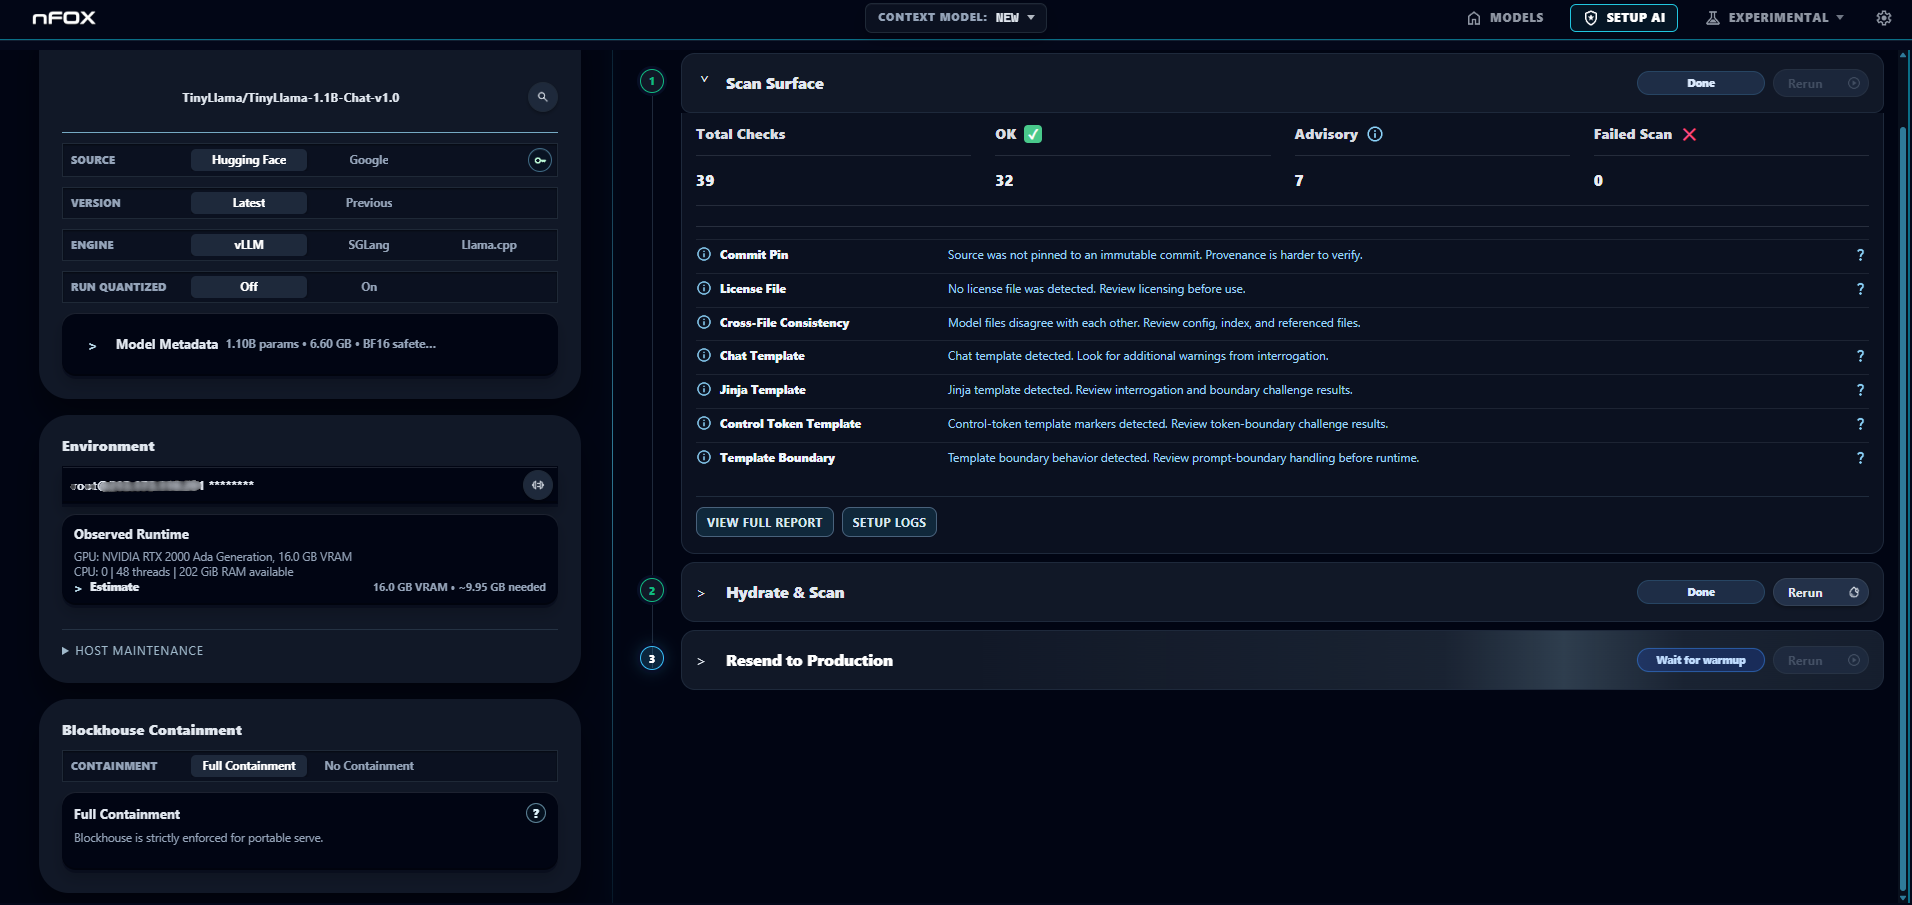
Kernel-enforced sandbox restricts AI workload privileges while the nFOX Platform enables fleet management across enterprise-controlled GPU infrastructure
NEW YORK, NY, UNITED STATES, October 15, 2026 /EINPresswire.com/ — nFOX Lab, a leading developer of AI runtime and model security technology for enterprises, today announced plans to open source Blockhouse, its kernel-enforced AI workload sandbox, and launched the nFOX Platform for deploying and managing open AI models on infrastructure enterprises control. Blockhouse is available in beta for qualified enterprise evaluations.
As enterprises introduce AI into private workflows, they need to strictly control permissions. Blockhouse addresses these needs by stripping away privileges from AI workloads by default, restoring permissions only in a controlled and deliberate manner through enterprise-defined policies. nFOX allows customers to manage their fleet of privately contained AI.
“Companies need a practical way to run AI models without giving up control of their systems and data,” said Gordon Allott, founder and CEO of nFOX. “NVIDIA’s Open Shell reflects the same architectural principle behind our approach: privileges should be denied by default and granted only through explicit enterprise controls. We developed Blockhouse to put clear boundaries around what AI workloads can access and do. The nFOX Platform helps teams manage those deployments and review integrity checks and containment events, giving them the evidence they need to make informed adoption decisions.”
Containment built into the runtime
Blockhouse enforces the sandbox boundary at the kernel level, below the application layer. Model runtimes operate inside the sandbox with only approved access. Attempts to operate outside that boundary are blocked, halted, and recorded.
Traffic passes through Porthole, a kernel-policed, audited communication channel. Runtime credentials and audit controls remain outside the model process. Approved model files are sealed with SHA-256 hashes before serving, and ongoing integrity checks halt serving when changes to those files are detected.
The sandbox supports vLLM, SGLang, and llama.cpp, applying the same containment boundary and monitored channel across supported serving engines. Each run records sandbox health and approved access. Blockhouse also reports when a host cannot provide the expected protection.
Fleet management inside the enterprise
The nFOX Platform provides an enterprise-controlled console to evaluate, deploy, and monitor models on customer-selected GPU infrastructure, including cloud virtual machines, rented GPU hosts, and on-premises Linux servers with NVIDIA GPUs. Teams can manage multiple models on a host and select supported serving engines and quantization modes.
The platform brings model approval and ongoing operational oversight into a consistent workflow:
• Evaluate and approve: Check model configuration, tokenizer, and code-execution flags, verify file integrity, and test contained models with adversarial prompts.
• Deploy and serve: Run approved models inside Blockhouse and provide OpenAI-compatible API endpoints for production deployments.
• Monitor and review: Track requests, integrity checks, and containment events, with runtime evidence available to existing EDR and SIEM workflows.
“Security teams need to understand the boundary around an AI workload and see how it behaves during operation,” said Chris Egloff, CTO of nFOX. “Blockhouse combines enforceable access restrictions with reviewable evidence, helping teams evaluate models and investigate containment events.”
Open source Blockhouse
nFOX plans to release Blockhouse as open source, allowing developers and enterprise security teams to inspect the implementation and evaluate its containment approach on infrastructure they control. Blockhouse provides the workload sandbox, while the nFOX Platform adds a centralized environment for managing model deployment and operational oversight across enterprise GPU hosts.
The nFOX Platform is available now. Blockhouse is available in beta for qualified enterprise evaluations. To request a demonstration or discuss deployment requirements, visit https://www.nfoxlab.com/contact.
About nFOX
nFOX develops AI runtime and model security technology for enterprises running open models on infrastructure they control. Its Blockhouse sandbox provides kernel-enforced containment, integrity checks, and reviewable runtime evidence. The nFOX Platform helps teams evaluate, deploy, and manage those workloads through an enterprise-controlled console. Learn more at https://www.nfoxlab.com/.
Sarah Thorson
Ripple Communications
Visit us on social media:
LinkedIn
Legal Disclaimer:
EIN Presswire provides this news content “as is” without warranty of any kind. We do not accept any responsibility or liability
for the accuracy, content, images, videos, licenses, completeness, legality, or reliability of the information contained in this
article. If you have any complaints or copyright issues related to this article, kindly contact the author above.

Media gallery